01
Exact technical coverage
Service profiles show the controlled areas assessed, attacker or reviewer perspective, access required, evidence produced, applicability and limitations.
Damocles tests the attack surface, reviews applications and cloud environments, operates selected security controls, investigates material activity and helps customers complete difficult remediation. Governed technical services publish what is assessed, the evidence produced, relevant framework or control mappings and the boundary of the assurance. Guardian connects the findings, owners, actions and closure evidence behind that work.
A technical service should be more specific than a service name and a list of benefits. For governed assurance services, Damocles publishes the testing perspectives, controlled coverage areas, required access, evidence outputs, relevant methodology references and material limitations that define the engagement.
Where technical evidence is mapped to a security framework or control objective, the mapping is identified as directly assessed, supporting evidence or contextual. That gives security, risk and audit teams usable traceability without presenting a point-in-time technical engagement as certification or complete compliance.
Service profiles show the controlled areas assessed, attacker or reviewer perspective, access required, evidence produced, applicability and limitations.
Relevant approved methodologies, standards and control objectives are referenced according to how the engagement actually uses them.
Retesting, rescans, configuration review, source health, investigation outcomes or other agreed evidence are used to verify the result where included.
Engage one focused service or combine Damocles services and Guardian products into a recurring security operating model.
Validate external, internal, wireless, website and API attack paths using authorised testing, evidence, remediation priority and retesting.
Explore Penetration Testing →Review authentication, authorisation, business logic, data handling, secrets and security design with developer-ready findings.
Explore Secure Code Review →Assess cloud identity, privilege, network exposure, data, workloads, logging and resilience against the intended architecture.
Explore Cloud Security Review →Onboard sources, monitor health, triage alerts, investigate material activity, escalate required action and report through Guardian.
Explore Aegis →Operate endpoint security, supported patching, DNS policy and managed application protection for the agreed customer estate.
Browse managed products →Improve segmentation, firewall policy, remote access, routing, resilience, migrations, hardening and implementation safety.
Explore Network Security →The tools and specialists differ by problem. The customer should still receive a consistent path from evidence to reviewed outcome.
Use testing, review, monitoring and security sources to identify material exposure.
Confirm the finding, affected scope, evidence and practical consequence.
Focus on the changes that reduce the most meaningful attack paths and operational risk.
Patch, reconfigure, harden, train, investigate or engineer the required change.
Review retest, rescan, source state, evidence or operational outcomes.
Show what was reduced, what remains open and where another decision is required.
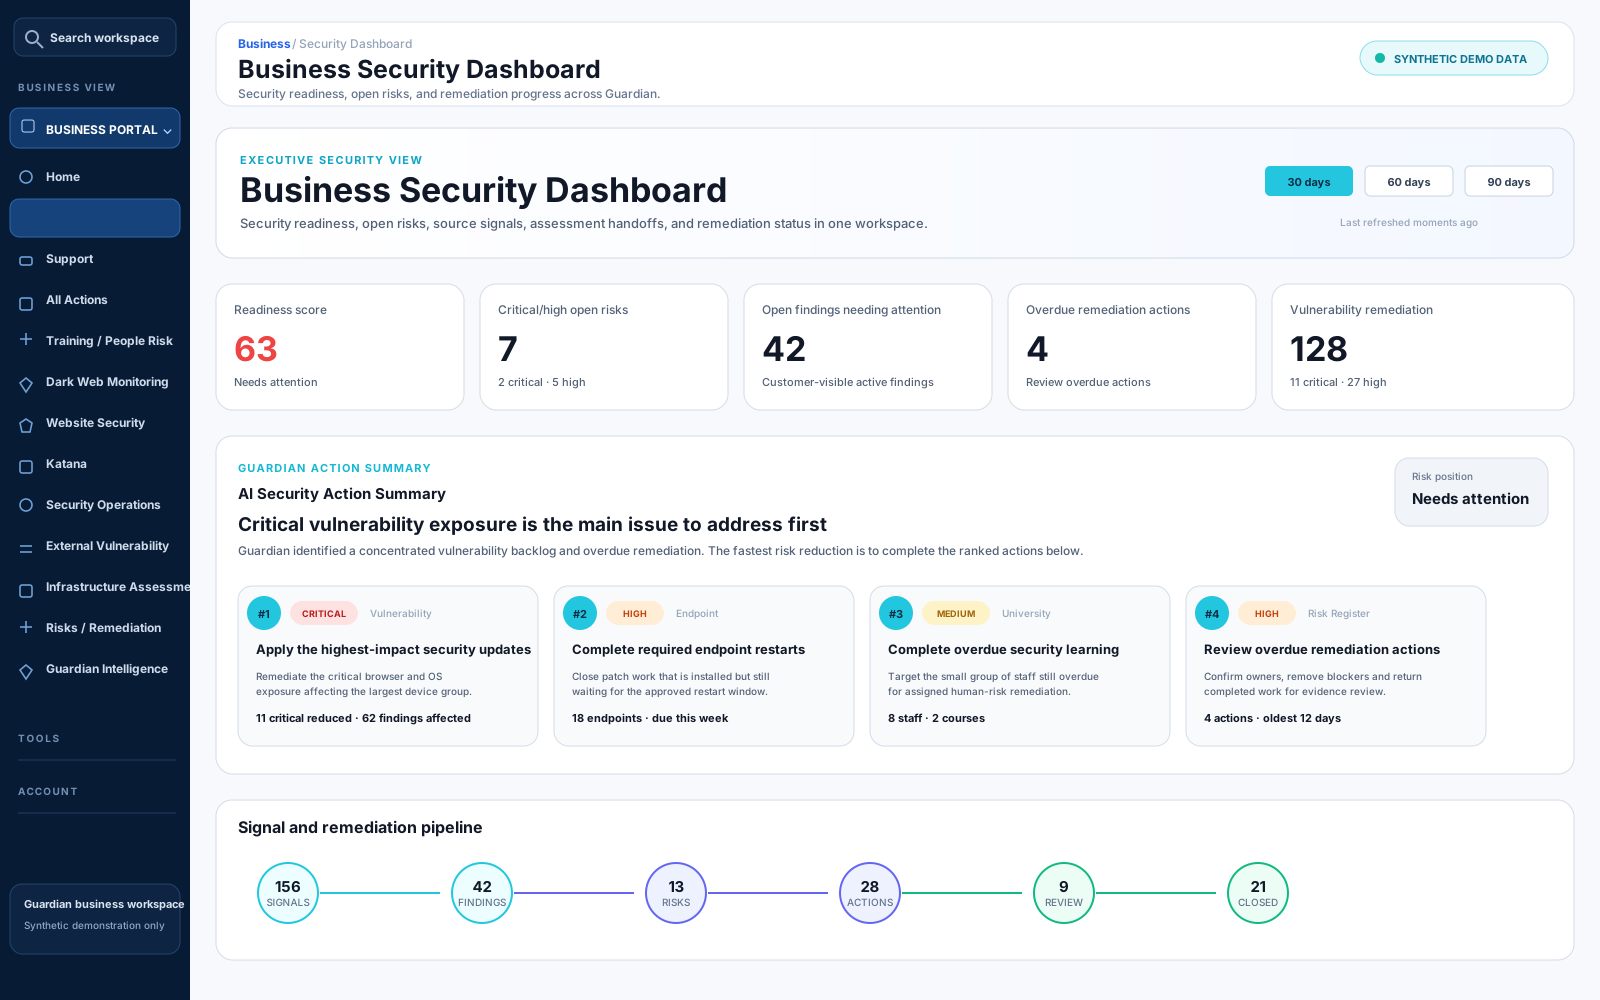
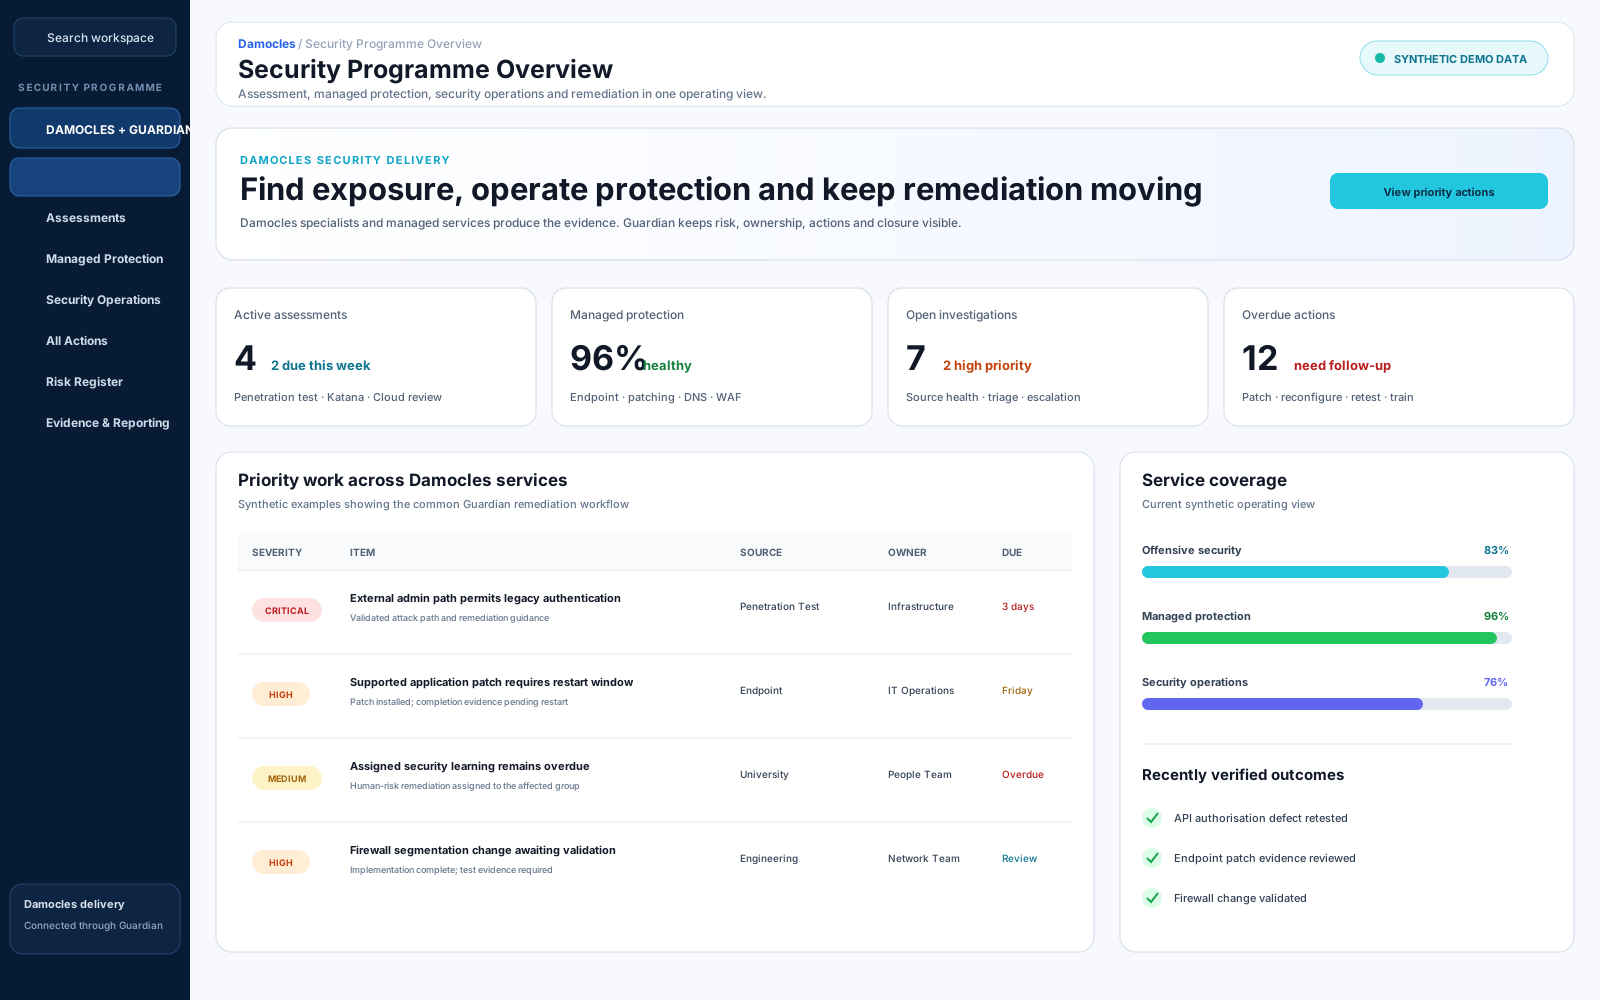
Damocles performs the testing, engineering, protection and managed security activity. Guardian gives businesses, internal teams and service providers one place to understand what was found, decide what matters, assign the work and retain evidence of the outcome.
A penetration-test finding, failed patch, dark web exposure, SOC investigation, overdue training assignment and firewall change can all move through a consistent risk, action and review lifecycle without pretending they are the same product.
See posture, risks, findings, actions, product health, investigations and reports in one governed view.
Assign the work to the right owner with due dates, source context and expected outcome.
Retain the retest, rescan, patch, configuration or investigation evidence used to review closure.
Use Guardian Core and selected Damocles services and products for staff, participants, websites, endpoints, risk, actions and evidence.
Explore NDIS and business use →Use Damocles for specialist testing, architecture, managed controls, operational escalation and difficult remediation.
Use provider-scoped customer workspaces, explicit product entitlements, consolidated Guardian wholesale billing and clear support boundaries.
Explore the partner model →Choose what you are trying to protect or improve and we will map the relevant Guardian capability, Damocles service and technical evidence.
Choose a plain-English security goal and the environment where it matters.
Receive no more than three controlled recommendations with a clear reason.
Reach Guardian, governed services, technical briefs and a prequalified next action.
We will identify whether the right next step is assessment, engineering, managed protection, security operations, incident readiness or a Guardian package—and explain the scope before work begins.